Nmap Cheat Sheet 2026: Every Command You Actually Need

Nmap Cheat Sheet 2026: Every Command You Actually Need

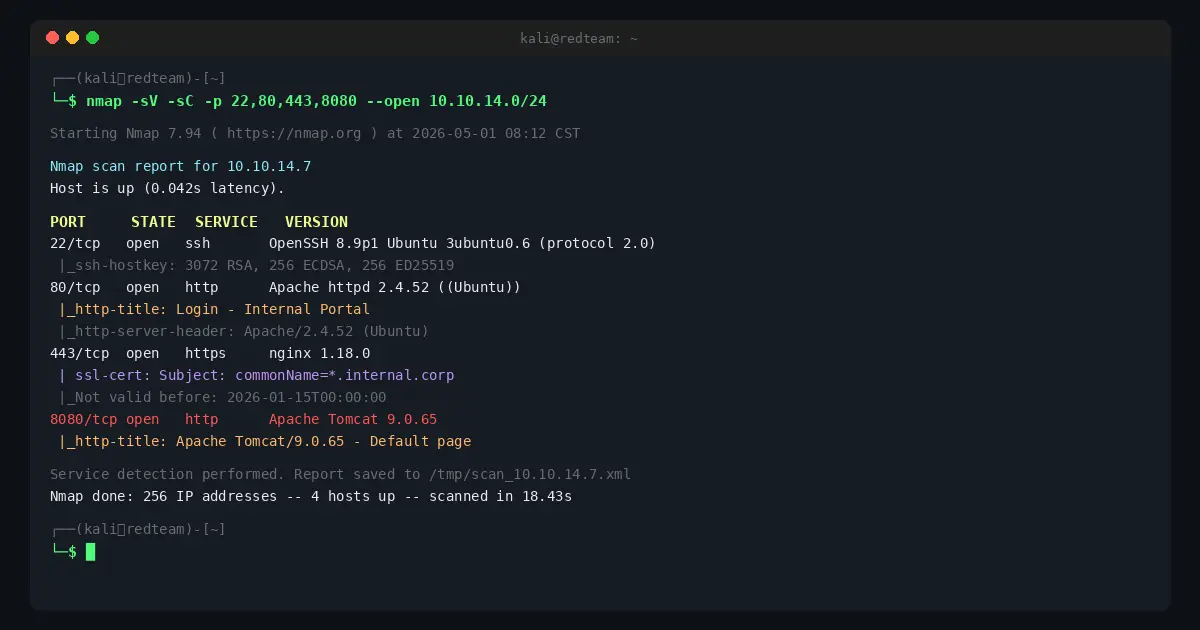
You don’t memorize Nmap. Nobody does. You keep a cheat sheet, you use it constantly, and eventually the important stuff sticks. This is that cheat sheet — updated for 2026, organized by what you actually do on engagements, not alphabetically by flag name. Covers everything from basic discovery to NSE scripting to firewall evasion. If it’s not here, you probably don’t need it in the field. Target Specification These go at the end of any Nmap command. Mix and match as needed. ...
May 1, 2026 · 10 min · Red Team Guide
eJPT Review 2026 - Is it worth it for beginners?

eJPT Review 2026: Is It Worth It for Beginners?

Every week someone asks me what certification to start with. Not what to get after two years of HTB and home lab practice. Not what comes after OSCP. The first one — the one for people who know they want to break into offensive security but don’t know where to start. My answer in 2026 is still the eJPT. Not because it’s prestigious. Not because it’ll make a hiring manager’s eyes light up. Because it does something more important than that: it teaches you what a penetration test actually feels like, before you’re in over your head. ...

April 28, 2026 · 8 min · Red Team Guide
VPS vs Home Lab for Security Practice

VPS vs Home Lab: Which is Better for Security Practice in 2026?

If you’ve spent any time in offensive security communities, you’ve seen the debate: build a home lab vs spin up a VPS and call it a day. Both camps have loud advocates, and both camps are partially right. I’ve run dedicated home labs for years, and I’ve also done engagements and personal research entirely on cloud infrastructure. Neither is universally better. The right answer depends on what you’re trying to learn, your budget, your living situation, and — critically — your threat model for legal exposure. ...

April 10, 2026 · 10 min · Red Team Guide

7 Best Penetration Testing Books 2026 (Ranked by an OSCP-Certified Red Teamer)

This list comes from 14+ years in offensive security — OSCP, CISSP, hundreds of engagements. Affiliate links help keep this site running. Every book here I’ve personally read and would hand to someone joining my team. There are two kinds of “best hacking books” lists. The first kind is a roundup of books someone found on Amazon and ranked by star rating. The second kind is a list from someone who’s actually used these resources on real engagements, in real prep for real certifications, with real clients waiting on the other end. ...

April 6, 2026 · 7 min · Red Team Guide

Best Penetration Testing Books & Tools (2026 Recommendations)

Written by a certified security professional (CISSP, OSCP) with 14+ years in offensive security and security leadership. Affiliate links help keep this site running — we only recommend resources we’d use ourselves. Every month there’s a new “best hacking books” list that looks like it was written by someone who Googled “cybersecurity books” for 20 minutes. This isn’t that. This is the list I’d hand to someone joining my red team. Books I’ve read cover to cover. Tools I reach for on real engagements. Gear that’s been through lab abuse and field use. If it’s here, it earns its place. ...

April 6, 2026 · 6 min · Red Team Guide
PNPT certification review 2026 - TCM Security

PNPT Certification Review 2026: Is TCM Security's Exam Worth It?

The OSCP used to be the only certification that mattered for penetration testers. Then TCM Security released the PNPT and changed the conversation. In 2026, the PNPT has become one of the most respected entry-to-mid-level certifications in offensive security — not because of brand recognition, but because of what the exam actually tests. This is a full review of whether it belongs in your certification roadmap. What Is the PNPT? The Practical Network Penetration Tester (PNPT) is a certification from TCM Security , created by Heath Adams (The Cyber Mentor). It’s a fully practical exam — no multiple choice, no CTF flags, no memorization. ...

April 1, 2026 · 6 min · Red Team Guide
AI-assisted penetration testing workflow 2026

AI-Assisted Pentesting: A Practical Guide for 2026 (Junior & Senior)

Claude just found 500 zero-days in production software. Kali Linux now has a native AI integration. Every security vendor is slapping “AI-powered” on their marketing page. And you’re sitting there thinking: okay, but where do I actually start? This guide is for you — the practicing pentester who knows their craft, understands the methodology, but hasn’t figured out how to meaningfully integrate AI into real engagements. We’ll cover the full kill chain, with concrete prompts, real tools, and honest assessments of where AI helps versus where it still fails. ...

March 29, 2026 · 12 min · Red Team Guide

Hack The Box vs TryHackMe: Which Platform is Better in 2026?

If you’re trying to break into offensive security — or level up your existing skills — you’ve probably been told to “just practice on HTB or THM.” Good advice. But which one? And for what? I’ve used both platforms extensively. Here’s the honest breakdown, based on what actually matters for building real-world penetration testing skills. The Short Answer TryHackMe is better for beginners and structured learners Hack The Box is better for intermediate-to-advanced practitioners and job prep Most serious practitioners use both Now let’s get into why. ...

March 28, 2026 · 6 min · Red Team Guide

How to Build a Home Pentest Lab on a Budget (2026 Guide)

A home lab is the single highest-leverage investment you can make in an offensive security career. Online platforms are great, but nothing replaces the muscle memory you build configuring, breaking, and rebuilding your own environment. The good news: you don’t need to spend thousands. A functional pentest lab in 2026 can be built for under $300 — and if you already have a decent laptop, possibly for free. This is the guide I wish I’d had when I started. ...

March 28, 2026 · 11 min · Red Team Guide

Red Team Career Path 2026: Levels, Salaries & Certs That Actually Matter

People talk about “getting into cybersecurity” like it’s a single destination. It isn’t. The red team career path is a long road with distinct phases, each requiring different skills, different mindsets, and different investments. I’ve spent over a decade in offensive security - from junior analyst writing first-ever pentest reports to leading red team programs and advising on enterprise security strategy. Here’s an honest map of the terrain. The Career Levels (And What They Actually Mean) Level 1: Junior Penetration Tester / Security Analyst (0-2 years) This is where everyone starts, and most people underestimate how much work it takes to get here legitimately. ...

March 28, 2026 · 8 min · Red Team Guide