Business Logic Vulnerabilities Attack Guide 2026: Detection, Exploitation & Bypass

Business logic vulnerabilities are the ones that slip through scanners completely. No CVE, no exploit-db entry, no Nuclei template. Just a gap between what the application intends to do and what it actually does when you push it sideways. They’re also some of the most valuable findings you can report. High business impact, hard to auto-detect, and often sitting in production for years because nobody thought to test them. This guide covers how to find them, how to exploit them, and what real business logic attacks look like in practice. ...
October 9, 2026 · 10 min · Red Team Guide

XXE Attack Guide 2026: XML External Entity Injection Detection, Exploitation & Bypass

XML External Entity (XXE) injection is one of the most dangerous web application vulnerabilities — capable of reading server files, triggering SSRF, and achieving remote code execution in the right conditions. It’s been in the OWASP Top 10 for years, and it’s still alive in production systems everywhere. The reason: developers enable XML parsers with external entity processing on by default and never turn it off. This guide covers detection, exploitation, out-of-band data exfiltration, blind XXE, and WAF bypass — with payloads you can use in your next pentest. ...

September 18, 2026 · 9 min · Red Team Guide

CSRF Attack Guide 2026: Cross-Site Request Forgery Detection, Exploitation & Bypass

Cross-site request forgery is one of those vulnerabilities that sounds simple until you actually try to exploit it in a modern application. In theory: trick a user’s browser into making an authenticated request to a target site. In practice: CSRF token validation, SameSite cookie policies, and Referer checks have made it significantly harder — but not impossible. In 2026, pure CSRF is less common on major platforms, but it still shows up regularly in internal tools, legacy enterprise apps, custom-built APIs, and any application that implements CSRF protection carelessly. And when CSRF tokens are present but misconfigured, the bypass is often trivially easy. ...

September 11, 2026 · 13 min · Red Team Guide

XSS Attack Guide 2026: Cross-Site Scripting Detection, Exploitation & Bypass

Cross-site scripting has been broken for as long as the web has existed. In 2026, it still shows up everywhere — modern SPAs, legacy enterprise apps, AI-generated frontends with no output encoding, CMS platforms with half-baked sanitization. XSS is the kind of vulnerability that’s “easy” to dismiss until you see a session token extracted from a banking app or a phishing payload delivered from a trusted domain. This guide covers everything: how XSS works, the three main categories, detection with Burp and manual techniques, exploitation for real impact, filter bypass when WAFs and sanitizers are in the way, and DOM-based XSS which most people still get wrong. ...

September 8, 2026 · 10 min · Red Team Guide

SQL Injection Attack Guide 2026: Detection, Exploitation & WAF Bypass

SQL injection has been on the OWASP Top 10 since the list started. In 2026, it still breaks real systems. Poorly sanitized inputs, legacy codebases, ORM misconfigurations — the attack surface hasn’t gone away. If anything, the rise of AI-generated code has introduced new classes of injection bugs. This guide covers everything: how SQLi works, how to detect it, how to exploit it across all major categories, how to weaponize SQLMap, and how to bypass WAFs when they’re in the way. ...

September 4, 2026 · 11 min · Red Team Guide

Web Application Pentesting Guide 2026: Tools, Techniques & Methodology

Web application pentesting is where most red teamers spend the majority of their billable hours. It’s also where a huge chunk of real-world breaches happen — not through exotic exploits, but through the same OWASP Top 10 vulnerabilities that have existed for decades. This guide covers the full methodology: reconnaissance, mapping the attack surface, exploiting common vulnerabilities, and reporting findings. Whether you’re doing your first web pentest or sharpening your methodology for bug bounty, this is the process. ...

September 1, 2026 · 11 min · Red Team Guide

Top 10 Kali Linux Tools for Beginners (2026 Edition)

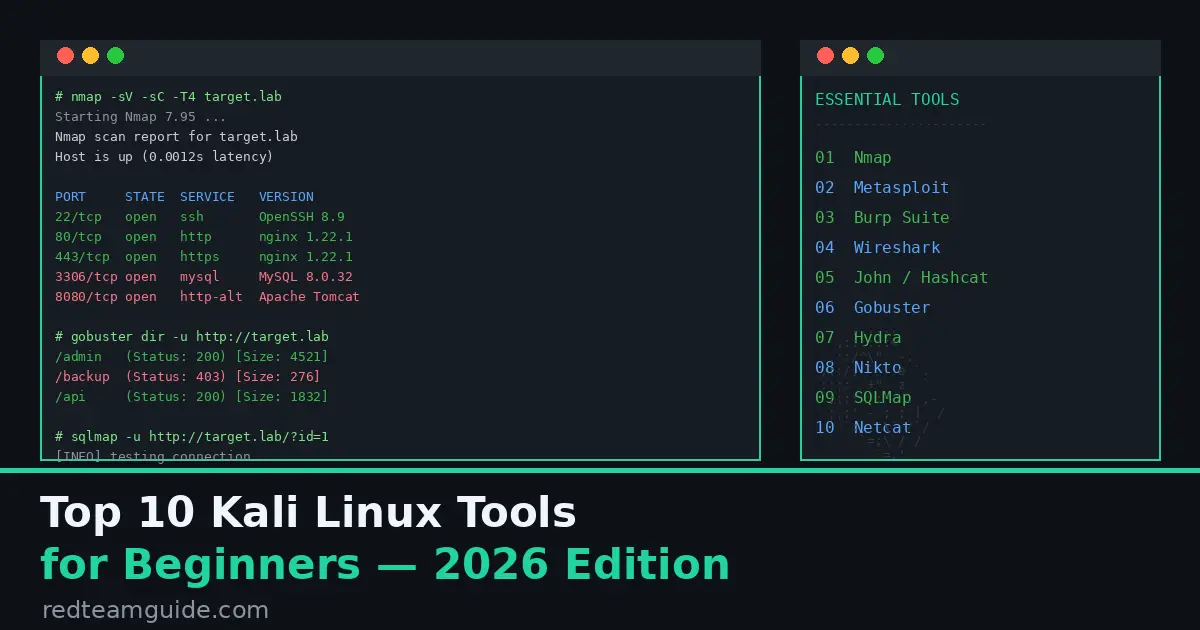
This article is written from 14+ years of offensive security practice. Some links are affiliate links that help keep this site running — I only recommend tools and services I’d use myself. Kali Linux comes loaded with over 600 security tools. If you’re new to penetration testing, that’s not empowering — that’s paralyzing. Here’s the honest truth: working pentesters don’t use most of what’s installed. They use a tight core of tools extremely well, and add specialized ones when a specific engagement calls for it. The practitioners who get hired aren’t the ones who can name every tool — they’re the ones who can actually use ten of them. ...

May 12, 2026 · 12 min · Red Team Guide
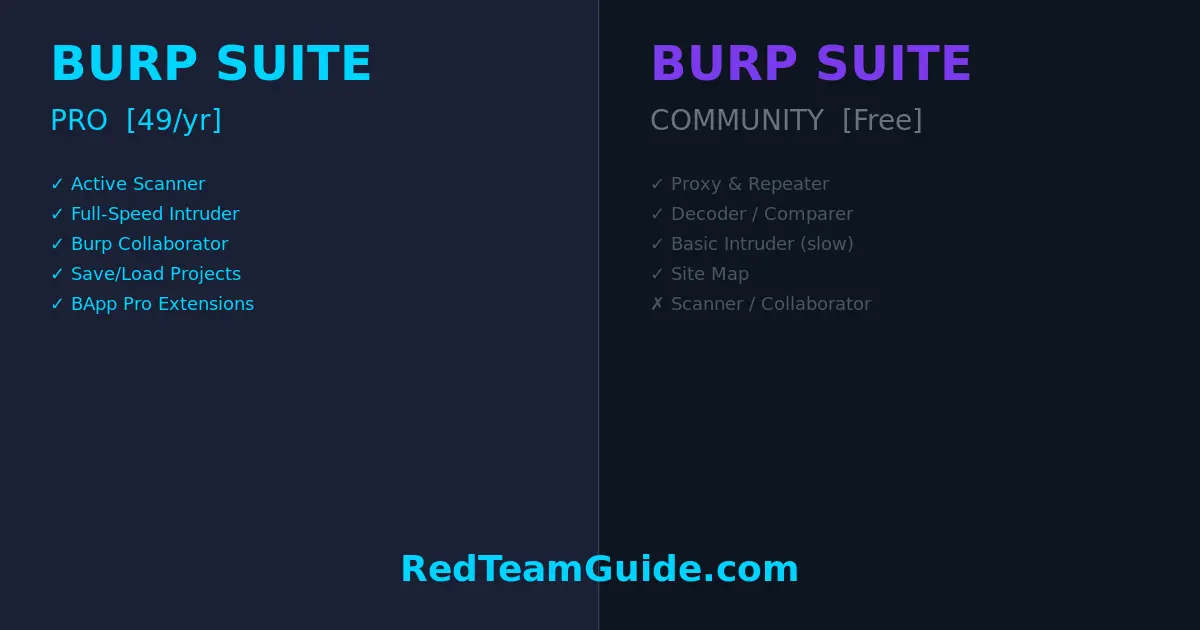
Burp Suite Pro vs Free

Burp Suite Pro vs Free: Is It Worth It for Pentesters in 2026?

Bottom line: If you’re doing professional web app pentests or bug bounty hunting seriously, Burp Suite Pro pays for itself after one engagement. If you’re learning or doing CTFs, Community Edition is genuinely sufficient — for now. What Is Burp Suite? Burp Suite is PortSwigger’s web application security testing platform. It’s been the industry standard for web app pentesting for over a decade, and for good reason — it intercepts, manipulates, and replays HTTP/S traffic with surgical precision. Whether you’re hunting for SQLi, IDOR, XSS, or chaining together complex multi-step attack sequences, Burp is the tool you’ll reach for first. ...

April 14, 2026 · 6 min · Red Team Guide